Anatomy of the EUR 100 Million Cyber Heist at Crédit Mutuel Arkéa
November 16, 2026
Crédit Mutuel Arkéa has confirmed an estimated EUR 100 million loss from the attack it suffered over 1 to 3 November - the largest cyber heist ever publicly disclosed by a European bank. The figure is not yet stabilised: the amount initially taken was higher, and part of it has been recovered or is in the process of being recovered. Client assets were untouched, the interruption of client operations lasted between one and one and a half days, and the bank observed no withdrawals or client departures.
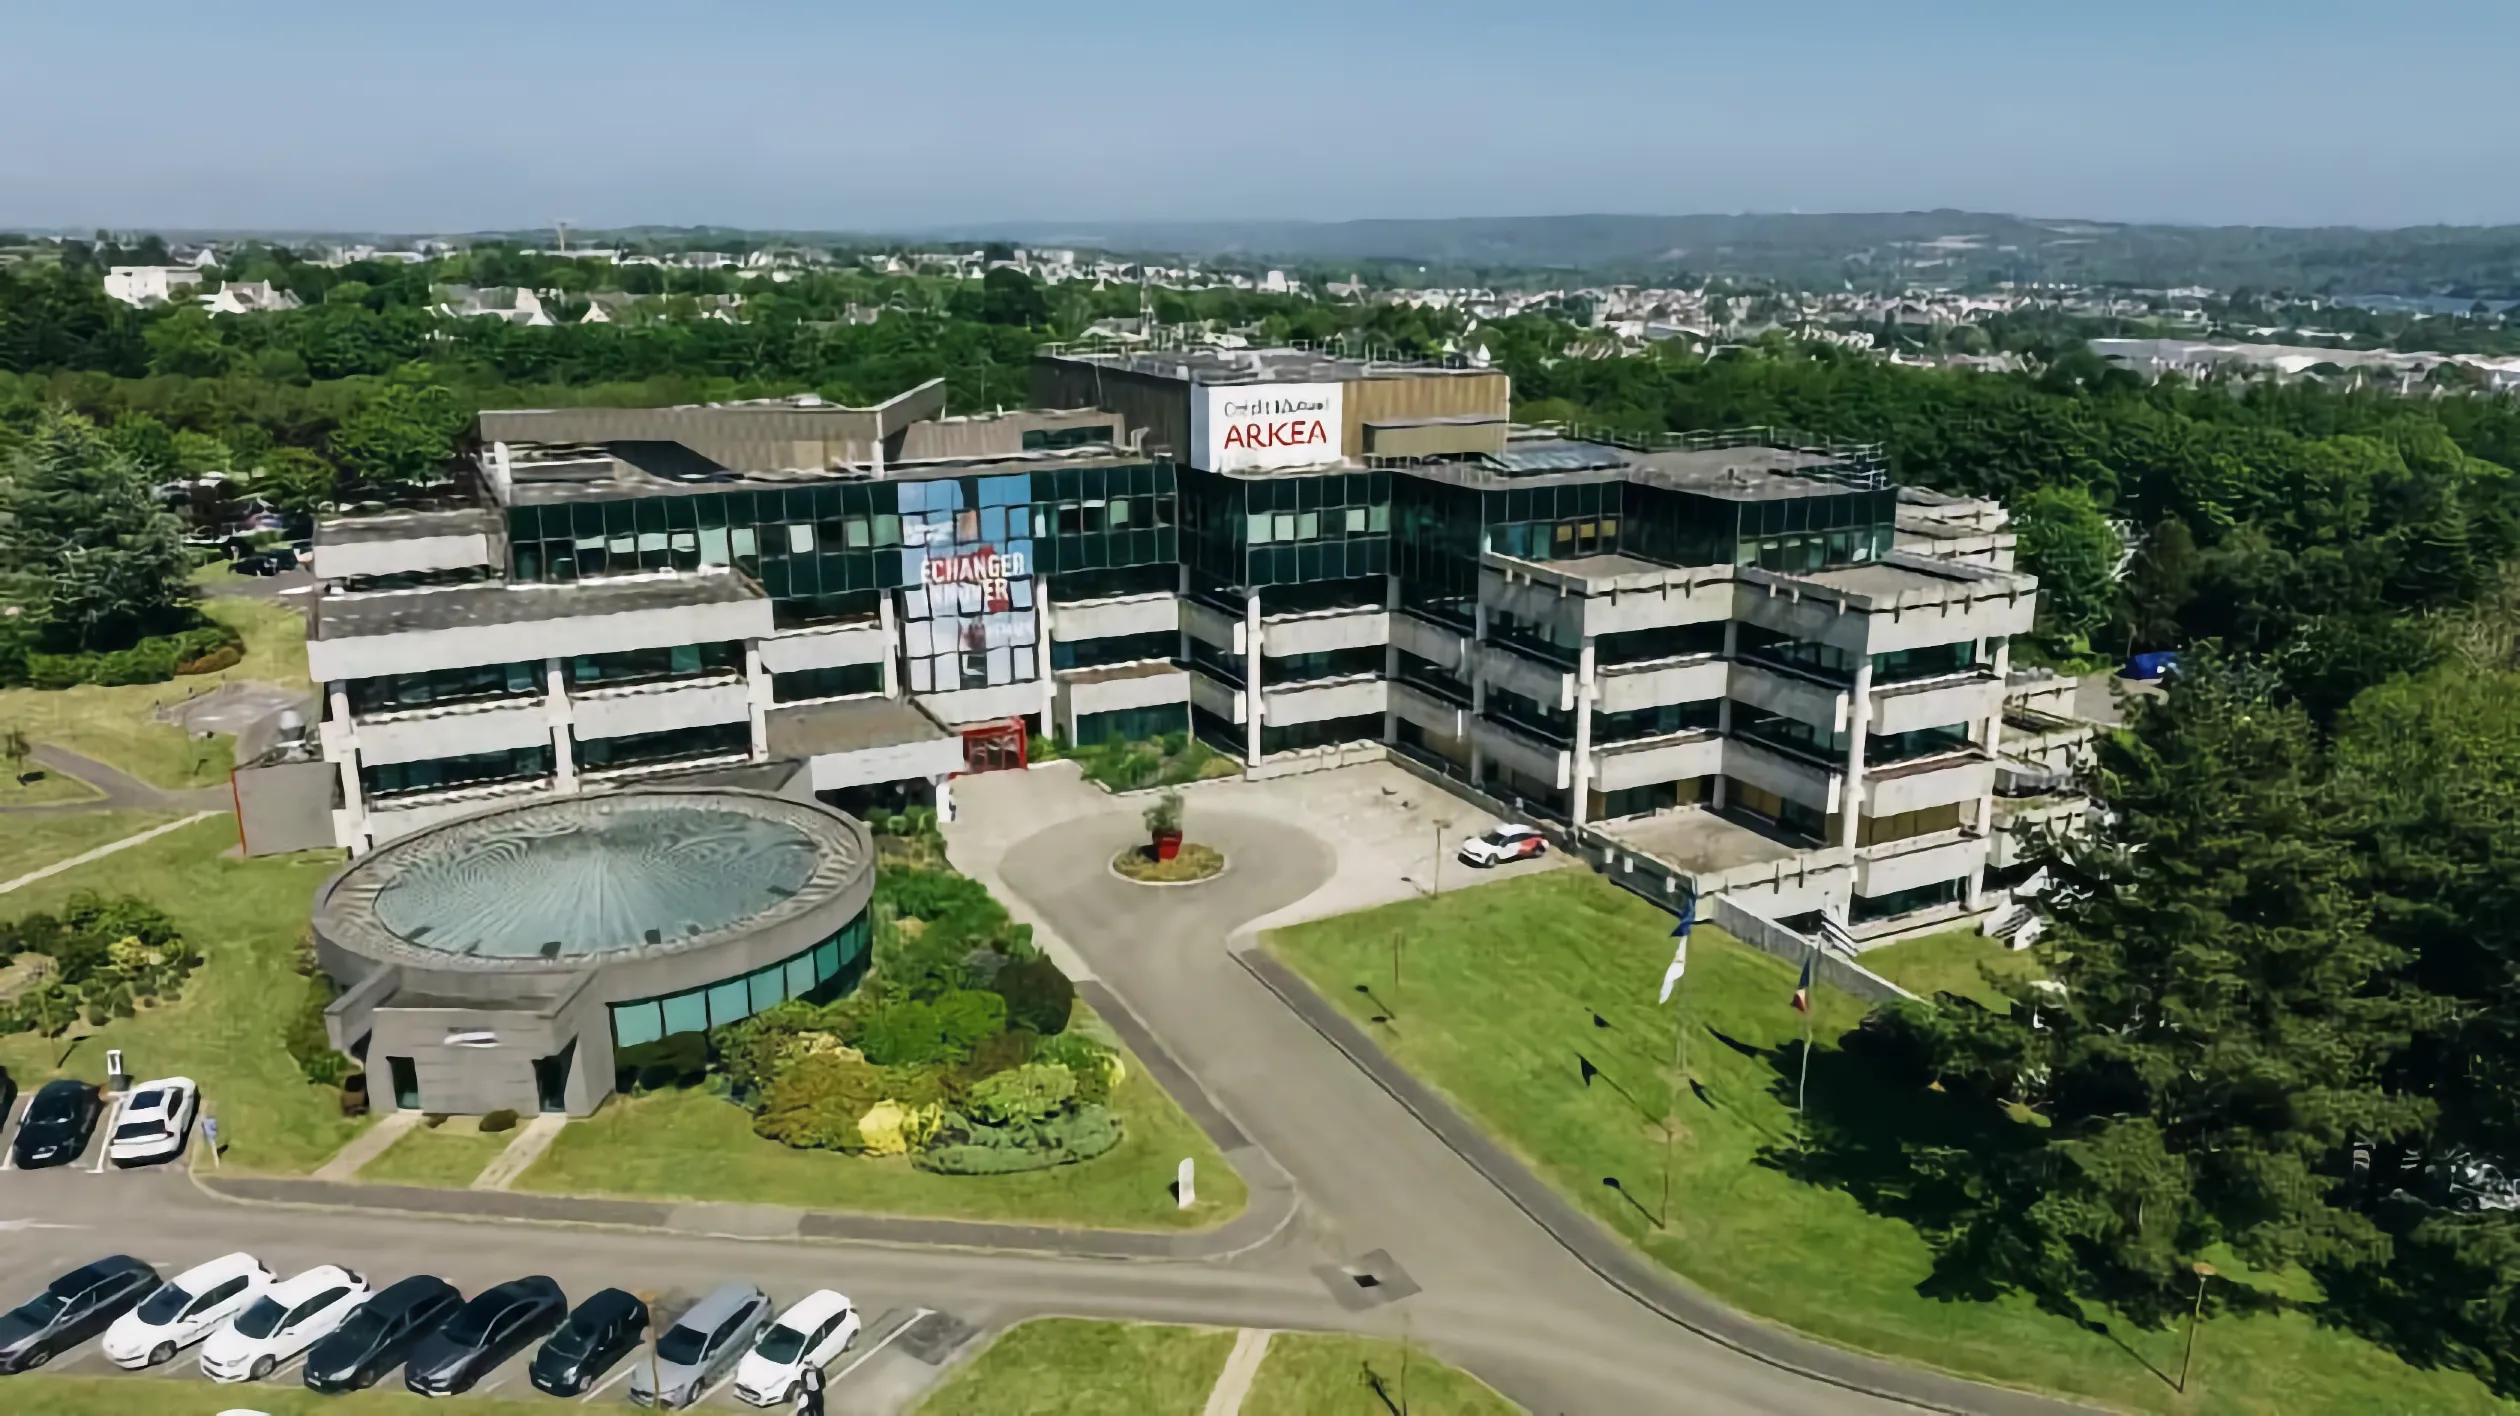
Two exclusive Les Echos articles - an interview with chairman Julien Carmona and a follow-up investigation - allow the attack chain to be reconstructed. It starts outside the bank’s perimeter. The week before the attack, the attackers exploited a flaw in the online SaaS application of a compliance-software publisher - used for fund onboarding, KYC and AML-CFT checks, and hosted on public cloud. That compromise yielded elements that defeated the bank’s authentication systems. The group’s investment subsidiary, Arkéa Capital, reportedly served as the entry point into the banking information system.
Julien CarmonaThe attack was highly sophisticated, made to defeat our controls. It is as if the attackers had obtained a bunch of keys, and the barriers came down.
Once inside, the attackers chained highly complex operations to create fake accounts with every appearance of legitimacy, and generated IBANs - some in the name of the Fortuneo online bank - to move funds out of Crédit Mutuel Arkéa’s own accounts. Fortuneo’s systems and clients were not concerned. The money then left via instant transfers, not SWIFT or SEPA, towards European banks, and from there towards crypto platforms. The unexplained movements were detected on the morning of 3 November; the bank isolated its systems, blocked flows to seal off the payment infrastructure, and had to purge traces spread throughout the information system before declaring the incident contained the next morning. The ECB, ACPR, AMF and ANSSI were notified as soon as the gravity of the incident was established. Public communication was deliberately deferred until the attack was mastered; the disclosure came on 4 November from blockchain analyst ZachXBT. The bank has since filed a criminal complaint with the prosecutor’s office, which has opened a judicial investigation conducted by the judicial police and the anti-cybercrime unit (OFAC). To date there is no solid element on the origin of the attackers, and no indication of internal collusion, though Carmona concedes the investigations will explore every avenue.
The identity of the compromised provider is being deliberately withheld. Carmona describes this as a collective decision of the banks: naming it is not in the public interest, and similar providers could then be targeted. The name was shared with other banks, and to the bank’s knowledge no other bank working with the provider has had its keys obtained. In the follow-up investigation, Les Echos goes further: according to multiple sources, the provider is a French publisher of subscription-based compliance software for asset managers and private equity professionals, acquired at end-2025 by a Belgian group, with some 80 claimed clients.
The bank attributes two characteristics to the operation that should concern every CISO: speed and sophistication consistent with the support of advanced AI models, and preparation over months. Carmona is explicit that even with strict internal and external audit of providers, residual security flaws and update delays remain exploitable. The ECB had indeed sounded the alarm on cyber risk from frontier AI models and required all banks to roll out action plans for prevention, detection and response - but full application was only due on 1 January 2027, and implementation was still under way. The scenario had not been tested as such in the ECB’s cyber stress tests: an attack path that neither the institutions nor the supervisory authorities had anticipated.
DORA, Carmona concedes, is a good regulation - his point is that the collective reflection should now harden requirements further. In France, the cyber resilience bill covering the national transposition of DORA and NIS2 is still under examination. His own numbers underline the limits of spending as a defence: IT and digital at 12% of net banking income (some EUR 300 million, above the roughly 10% sector average), a cyber budget up 70% over four years - and still the first French bank to be compromised in this manner.
Learn more Read the coverage by Les Echos (in French): the interview with Julien Carmona Opens in a new tab and the exclusive on the compromised provider Opens in a new tab .
